

Table of Contents
- What Secure Mobile Payment Processing Solutions Actually Include
- How Mobile Payment Processing Works: Authorization, Tokenization, and Encryption
- PCI DSS Compliance for Mobile Payments: What Your Business Must Verify
- How to Accept Mobile Payments Securely: A Step-by-Step Setup
- Mobile Credit Card Reader Security Features That Matter
- Transaction Fees, Hidden Costs, and Cross-Border Mobile Payment Considerations
- Comparing Secure Mobile Payment Processing Solutions: A Decision Table
- Conclusion: Choosing the Right Secure Mobile Payment Partner
- Frequently Asked Questions
Last Updated: September 23, 2026
What Secure Mobile Payment Processing Solutions Actually Include
Secure mobile payment processing solutions are the hardware, software, and security protocols that let a business accept card and digital wallet payments on a phone or tablet while protecting cardholder data at every step. This guide from Merchant Card Advisors breaks down what actually matters when you choose one.
Hardware Readers vs. Software-Only (SoftPOS) Options
A hardware reader is a physical device that pairs with your phone or tablet over Bluetooth or a dock. It handles the card read and encrypts data at the point of capture. SoftPOS turns a compatible phone or tablet into the terminal itself, using the device’s built-in NFC chip to accept tap-to-pay with no extra hardware.
The trade-off is straightforward:
- Hardware readers cost more upfront but work with almost any phone and offer a familiar checkout flow.
- SoftPOS cuts equipment cost to near zero but depends on device compatibility and a stable app.
- Hardware readers tend to suit high-volume counters; SoftPOS suits mobile and pop-up sellers.
How Mobile Payment Processing Works: Authorization, Tokenization, and Encryption
Every mobile transaction runs through the same core sequence: capture, encryption, authorization, and settlement. Understanding it helps you ask better questions of any provider.
- Card capture. The reader or device captures the card data at the point of sale.
- Encryption. Data is encrypted immediately, before it leaves the device.
- Tokenization. The card number is replaced with a token, a stand-in value with no usable card data.
- Authorization. The token and transaction details go to the payment gateway for real-time authorization.
- Settlement. Funds move through the merchant account to your bank.
Tokenization and End-to-End Encryption Explained
Tokenization replaces a card number with a unique token that only your payment provider can map back to the real number. If a breach exposes the token, it’s useless to a thief.
Ask any provider two questions: “Is card data tokenized before it hits your servers?” and “Is encryption end-to-end, or does it break somewhere in the middle?” The answers separate serious processors from the rest.
PCI DSS Compliance for Mobile Payments: What Your Business Must Verify
PCI DSS compliance for mobile payments means your setup meets the Payment Card Industry Data Security Standard for handling card data. The level of validation depends on your transaction volume, not the size of your business.
The practical checklist for mobile acceptance:
- Confirm your reader or SoftPOS app is listed as a validated payment solution
- Verify the provider handles tokenization so your systems never store raw card numbers
- Complete the self-assessment questionnaire your provider or acquirer assigns
- Keep software and firmware updated on every device that touches payments
- Train staff on card capture and data handling basics
How to Accept Mobile Payments Securely: A Step-by-Step Setup
Setting up secure mobile acceptance takes a defined sequence. Skipping steps is how businesses end up with reconciliation headaches or compliance gaps.
- Choose hardware or SoftPOS based on your sales environment.
- Open a merchant account through a provider or acquirer suited to your industry.
- Complete underwriting, which is where hard-to-place sectors need the most help.
- Configure the payment gateway and connect it to your bank account.
- Test with a small transaction before going live.
- Train staff on refunds, voids, and secure card handling.
- Confirm your PCI validation is filed and current.
Integrating Mobile Payments With Your Existing POS or ERP
Integration is the step most guides skip, and it’s where hidden labor shows up. A provider that connects cleanly to your existing point of sale or ERP system means transactions post automatically; a poor fit means manual reconciliation at month-end, which is where small businesses quietly lose hours.
- Native integration. The gateway is already certified to work with your POS or ERP by name and version. This is the cleanest path: transactions, refunds, and settlement data flow into your system without custom work. Ask for the specific version number, not just the product name, because a certified integration can break on a major version upgrade.
- API integration. The gateway exposes a documented API so a developer can connect a custom or older system. This is the right path for businesses running bespoke software or a legacy POS the vendor no longer updates. Budget for developer time and for ongoing maintenance when the API changes.
- Middleware or file-based. A third-party connector or scheduled file export bridges the two systems. This is the fallback when neither native nor API options exist. It works, but it usually means batch reconciliation rather than real-time posting, so your books lag your sales.
Questions to ask before you sign:
- Does the gateway support my exact POS or ERP product and version?
- Is there a published API, and is it documented and versioned?
- How does transaction data flow into my accounting software, and in what format?
- Who supports the integration when it breaks, the gateway or the POS vendor?
- Are refunds, voids, and chargebacks posted back to the same system, or handled separately?
Before committing, ask for a sandbox or test environment and run one full cycle: sale, refund, and settlement. If the data doesn’t land in your accounting system correctly on the test, it won’t on live transactions either.
Mobile Credit Card Reader Security Features That Matter
The security features worth paying attention to are the ones that protect data at the moment of capture and prove it afterward. Everything else is marketing.
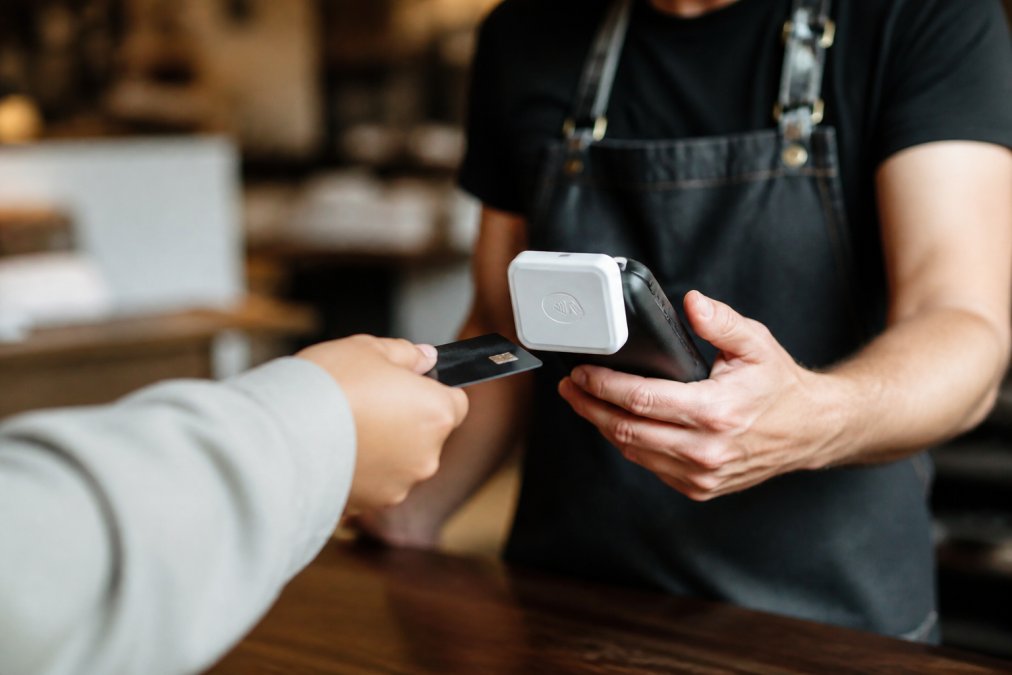
Look for these in any mobile card reader:
- Point-to-point encryption so card data is unreadable from swipe to processor
- Tokenization so no raw card number is stored
- Biometric authentication (fingerprint or face) to unlock the terminal and approve transactions
- Secure socket layer / TLS protection for data in transit
- Contactless and mobile wallet support for tap-to-pay and digital wallets
- Real-time fraud mitigation flags on unusual transactions
Transaction Fees, Hidden Costs, and Cross-Border Mobile Payment Considerations
Transaction fees are where the real cost differences hide, and where a “reasonable” quote can quietly cost more than it appears. To compare quotes honestly, you have to know which pricing model you’re being offered, because the same headline rate can produce very different effective costs at different volumes.
The Three Pricing Models You’ll Be Quoted
Flat rate (blended). One percentage plus a per-transaction fee on every card, regardless of card type. Easy to forecast, but you overpay on debit and basic credit cards, which cost the processor far less than the rate you’re charged. Flat-rate pricing tends to favor low-volume or very simple operations.
The Cost Layers Stacked on Top
Beyond the rate itself, watch for these line items:
- Interchange, set by the card networks and largely fixed
- Processor markup, the provider’s cut, which is negotiable
- Monthly fees, gateway fees, and statement fees
- PCI compliance fees, sometimes charged annually
- Batch and settlement fees per deposit
- Chargeback fees, which can run well above the transaction amount itself
- Equipment or app subscription fees, especially on SoftPOS plans that advertise “no hardware”
A common pattern is a low advertised rate paired with a high per-transaction fee, which punishes low-ticket sellers. Run your own average ticket and monthly volume through any quote before comparing it to another.
Cross-Border and Multi-Currency Costs
For cross-border sales, add multi-currency handling and currency conversion costs. When a customer pays in a foreign currency, someone absorbs the conversion spread, and it is usually the merchant unless you pass it through. Ask whether settlement lands in your domestic currency or the customer’s, and whether the conversion happens at the network rate or a marked-up rate.
The most common hidden cost is a rate that creeps up after the first few months. Ask whether the quoted rate is locked, whether the markup is fixed or variable, and get the answer in writing before you sign.
Request your last three statements and ask a prospective provider to reprice them line by line under interchange-plus. A provider that will do that math on your real numbers is showing you the actual cost, not a headline rate.
Comparing Secure Mobile Payment Processing Solutions: A Decision Table
The right choice depends on your sales environment, volume, and how much integration you need. Use this to match your situation to the right setup.
| Setup | Best For | Key Strength | Main Trade-off |
|---|---|---|---|
| Hardware reader | Retail counters, high volume | Certified, isolated card capture | Higher upfront cost |
| SoftPOS | Mobile, pop-up sellers | No extra hardware | Device-dependent |
| Gateway + custom POS | Businesses with existing systems | Clean integration, auto reconciliation | Setup complexity |
| ACH-based | Subscription billing | Lower per-transaction cost | Weaker consumer protections |
Before switching, request a line-by-line cost comparison against your last three statements. Providers that calculate real savings from your own numbers, not a generic percentage, are the ones worth trusting.
Conclusion: Choosing the Right Secure Mobile Payment Partner
The hard part isn’t finding a provider that accepts mobile payments. It’s finding one whose pricing holds up after month three and whose support answers at 2 AM. That’s where Merchant Card Advisors works differently: a full-service boutique approach, fair and honest pricing with no rate bumps, a vast network of bank partnerships for hard-to-place industries, and 24/7 personalized customer service from a real person.
Frequently Asked Questions
What security standards must mobile payment processors meet?
Mobile payment processors must comply with PCI DSS, the payment card industry’s data security standard. This covers encryption of card data in transit and at rest, tokenization so card numbers are not stored on the device, access controls, and regular vulnerability testing. When you choose a secure mobile payment processing solution, ask for its PCI DSS compliance level and confirm whether it handles tokenization on your behalf. That shifts most of the compliance burden away from your business.
How does tokenization protect mobile payment data?
Tokenization replaces a card number with a unique digital token at the moment of the transaction. The real card number never sits on your phone, tablet, or reader, so if a device is lost or stolen, there is no card data to expose. Tokens are useless outside the specific payment ecosystem that created them. Combined with end-to-end encryption, tokenization is one of the strongest defenses against data breach prevention failures in mobile payments.
What are the primary risks associated with mobile payment processing?
The main risks are card data exposure if encryption or tokenization is missing, fraud from stolen devices without biometric authentication or customer authentication, and compliance gaps that lead to fines or lost processing privileges. Hidden transaction fees and interchange rate surprises are a financial risk rather than a security one. Using a PCI DSS compliant mobile credit card reader and enabling tap-to-pay with biometric locks reduces most of these exposures.
What is the difference between mobile wallets and mobile card readers?
A mobile wallet stores payment credentials on a phone and uses tap-to-pay or contactless payments at checkout. A mobile card reader is a hardware device that plugs into or pairs with a phone or tablet so you can accept card payments on the go. Many secure mobile payment processing solutions support both. The reader handles card capture and encryption; the wallet handles customer authentication. Choosing between them depends on whether you are the merchant or the buyer.

